The Austrian Federal Government recently presented a revised draft of the NISG 2026 (we reported on the latest amendments). At the beginning of December, the new draft successfully passed the Internal Affairs Committee. Despite ongoing criticism regarding the competent authority and the lack of an external parliamentary review of the new draft, the plenary of the National Council has today also approved it with the required two-thirds majority. The adopted amendment proposal only slightly adapted the information obligations of the NIS-2 authority. It is positive that the cybersecurity authority is intended to act according to the principle of advising rather than penalising.
The adoption is a key step in Austria's national implementation of the NIS-2 Directive. Following the expected approval by the Federal Council and publication in the Federal Law Gazette, a nine-month transitional period will begin – after which companies must register with the NIS-2 authority and the full range of obligations will apply in autumn 2026.
Need for action for companies
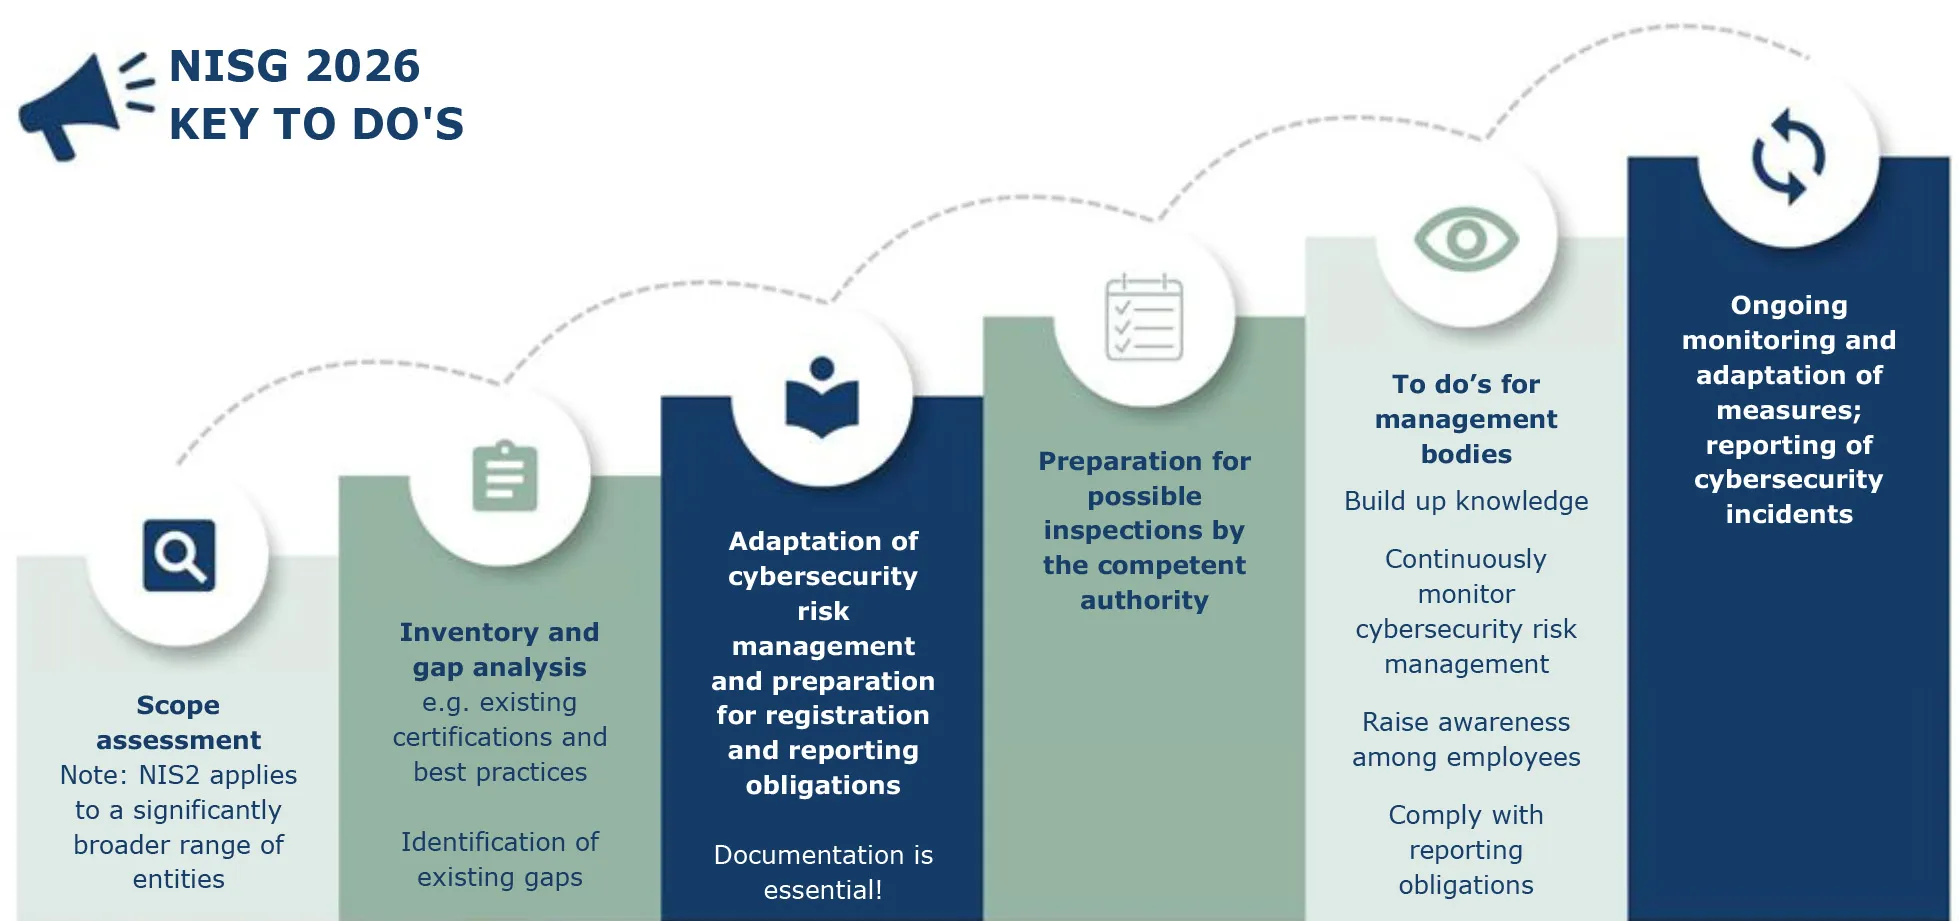
In this context, interactions with the Cyber Resilience Act and the Data Act, as well as parallel reporting obligations, for example under the GDPR, must also be taken into account. Your NIS-2 experts at DORDA will be pleased to support you in a targeted and efficient manner with their extensive experience and practical know-how. We will, of course, continue to keep you informed of further developments.